

 Jobs Home
 Cities
 Govt Depts
 Comapnies
 Industries
 Professions

| Sr. No | Post Name | No. of Jobs | Qualification | Other detail |
|---|---|---|---|---|
| 1 | Unit Head | 1 | Male |
Details of Job Advertisement by National Bank of Pakistan NBP 20-Sep-2026
This job was posted on 20-Sep-2026 and has a last application date of 30-Sep-2026.
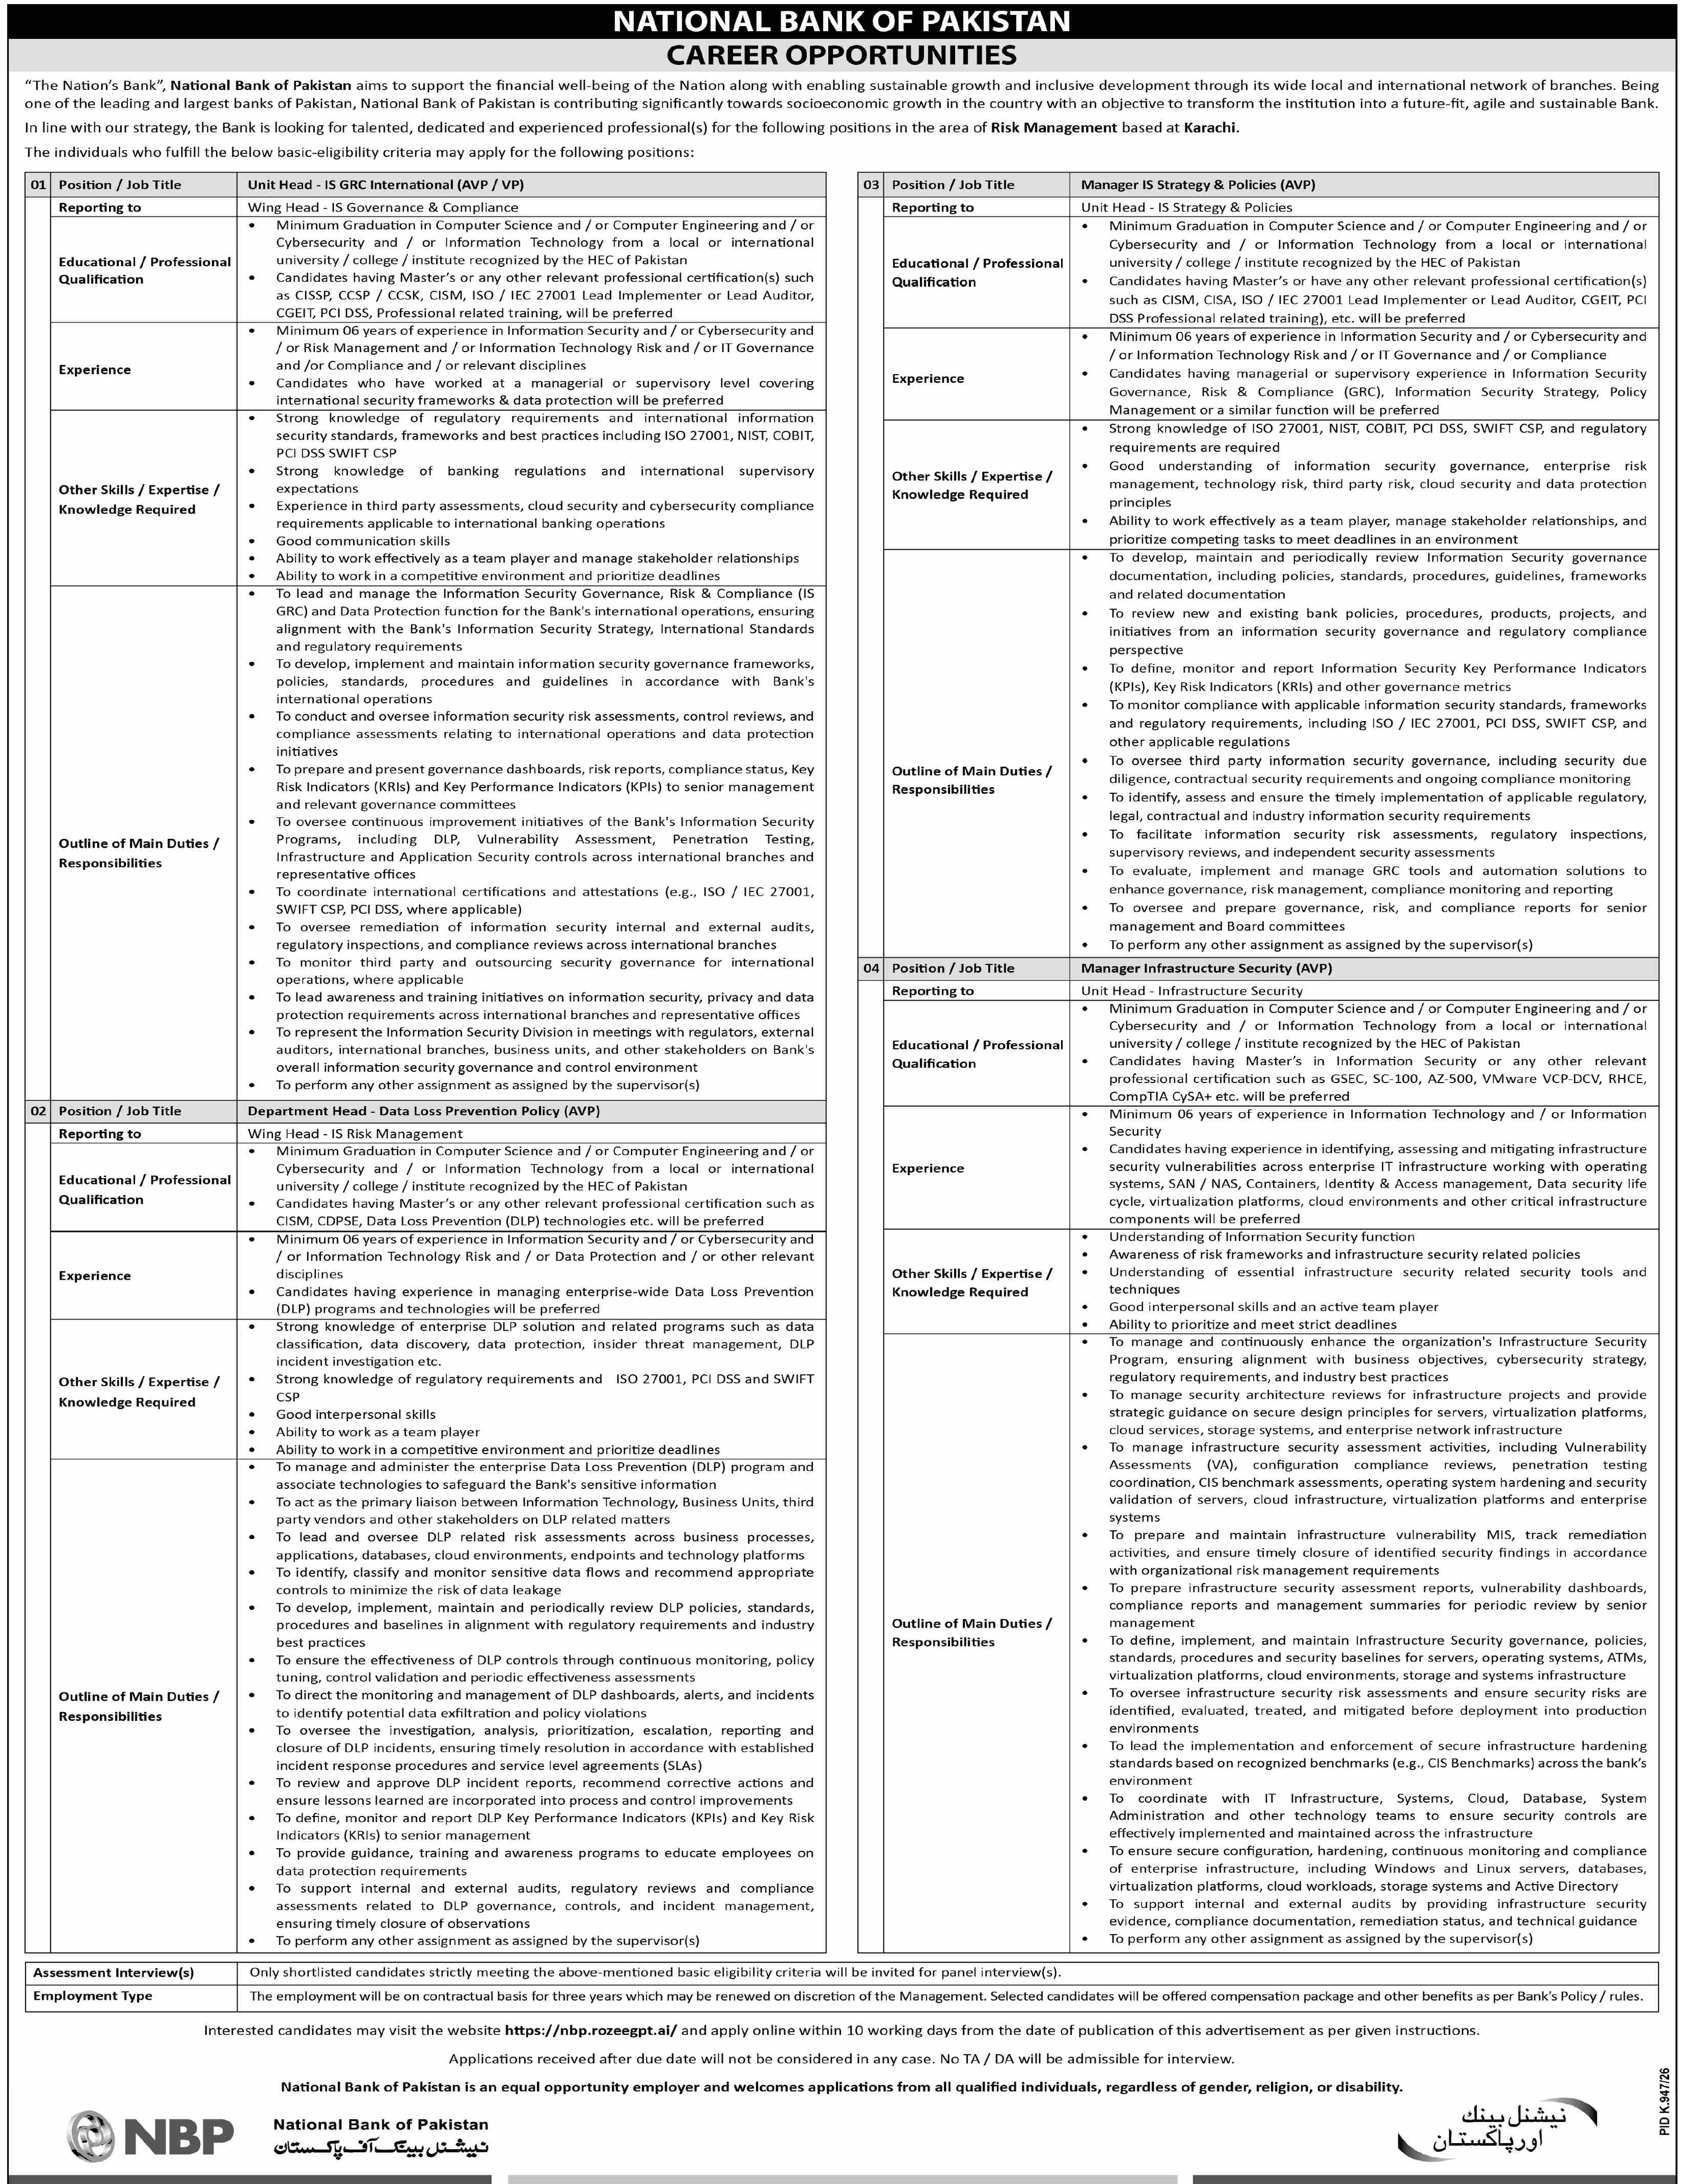
NATIONAL BANK OF PAKISTAN – CAREER OPPORTUNITIES
The Nation's Bank
National Bank of Pakistan, one of the leading and largest banks of Pakistan, is contributing significantly towards the socio-economic well-being of the nation. With a wide local and international network of branches, NBP is committed to sustainable growth and inclusive development.
In line with our strategy, we are seeking talented, dedicated, and experienced professionals for the following positions based at Karachi. The individuals who meet the basic eligibility criteria below may apply.
POSITION 1: Wing Head – IS Governance & Compliance (AVP/VP)
| Field | Details |
|---|---|
| Position/Job Title | Wing Head – IS Governance & Compliance |
| Reporting To | Unit Head IS GRC |
| Location | Karachi (Local and/or International) |
| Educational/Professional Qualification | Minimum Graduation in Computer Science and/or Computer Engineering and/or Cybersecurity and/or Information Technology from a local or international university/college/institute recognized by the HEC of Pakistan. Candidates having Master's or any other relevant professional certifications such as CISM, CISA, ISO/IEC 27001 Lead Implementer, or Lead Auditor, CGEIT, PCI DSS Professional, and/or related training will be preferred. |
| Experience | Minimum 10 years of experience in Information Security and/or Cybersecurity and/or Information Technology Risk and/or Governance and/or Compliance. Supervisory experience in Information Security is required. Candidates having experience in Governance, Risk & Compliance (GRC), Information Security Strategy, Policy, and Compliance are preferred. |
| Other Skills/Expertise/Knowledge Required | • Strong knowledge of ISO 27001, COBIT, NIST, PCI DSS, SWIFT CSP, and regulatory requirements. • Good understanding of managing technology third-party risk, cloud security, and data privacy principles. • Good communication and interpersonal skills. • Ability to effectively plan, manage stakeholder relationships, and prioritize competing tasks to meet deadlines is an essential requirement. • Ability to work independently and periodically. |
Outline of Main Duties:
-
To develop, implement, and maintain information security governance, including Information Security governance structures, guidelines, frameworks, and existing bank policies.
-
To monitor compliance with applicable information security governance and regulatory requirements, including ISO 27001, SWIFT CSP, PCI DSS, and other applicable regulations.
-
To oversee third-party information security governance, including security contractual security requirements and ongoing compliance.
-
To oversee the implementation of applicable local and international regulatory requirements.
-
To identify legal, contractual, and industry information security requirements.
-
To facilitate information security risk assessments, regulatory inspections, supervisory reviews, and independent security assessments.
-
To manage GRC tools and automation solutions across local and international branches.
-
To perform secretariat duties for management and Board committees.
POSITION 2: Manager IS Strategy & Policies (AVP)
| Field | Details |
|---|---|
| Position/Job Title | Manager IS Strategy & Policies |
| Reporting To | Unit Head IS Strategy & Policies |
| Location | Karachi |
| Educational/Professional Qualification | Minimum Graduation in Computer Science and/or Computer Engineering and/or Cybersecurity and/or Information Technology from a local or international university/college/institute recognized by the HEC of Pakistan. Candidates having Master's or any other relevant professional certifications such as CISM, CISA, ISO/IEC 27001 Lead Implementer, or Lead Auditor, CGEIT, PCI DSS Professional, and/or related training will be preferred. |
| Experience | Minimum 06 years of experience in Information Security and/or Cybersecurity and/or Information Technology Risk and/or Governance and/or Compliance. Supervisory experience in Information Security is preferred. Candidates having experience in Governance, Risk & Compliance (GRC), Information Security Strategy, Policy, and Compliance are preferred. |
| Other Skills/Expertise/Knowledge Required | • Strong knowledge of ISO 27001, COBIT, NIST, PCI DSS, SWIFT CSP, and regulatory requirements. • Good communication and interpersonal skills. • Ability to effectively plan, manage stakeholder relationships, and prioritize competing tasks to meet deadlines is an essential requirement. • Ability to work independently and periodically. |
Outline of Main Duties:
-
To assist in the development, implementation, and maintenance of information security strategy, policies, and procedures.
-
To monitor compliance with applicable information security governance and regulatory requirements.
-
To support internal and external audits, regulatory reviews, and compliance activities.
-
To perform information security risk assessments and gap analyses.
-
To manage and administer GRC tools and automation solutions.
-
To support the overall information security governance and control framework of the bank.
POSITION 3: Manager IS Security (AVP)
| Field | Details |
|---|---|
| Position/Job Title | Manager IS Security |
| Reporting To | Unit Head IS Security |
| Location | Karachi |
| Educational/Professional Qualification | Minimum Graduation in Computer Science and/or Computer Engineering and/or Cybersecurity and/or Information Technology from a local or international university/college/institute recognized by the HEC of Pakistan. Candidates having Master's or any other relevant professional certifications such as CISM, CISA, CISSP, DLP (Data Loss Prevention) technologies, etc., will be preferred. |
| Experience | Minimum 06 years of experience in Information Security and/or Cybersecurity and/or Information Technology Risk and/or Governance and/or Compliance. |
| Other Skills/Expertise/Knowledge Required | • Strong knowledge of ISO 27001, PCI DSS, SWIFT CSP, and related standards. • Good understanding of infrastructure security, including operating systems, databases, virtualization platforms, cloud environments, storage systems, and Active Directory. • Ability to work in a team and independently. • Understanding of security benchmarks across the bank. |
Outline of Main Duties:
-
To manage and administer information security infrastructure security controls, including configuration, compliance documentation, remediation, and technical guidance.
-
To conduct vulnerability validation of servers, shared drives, operating system hardening, and security platforms.
-
To support internal and external audits, regulatory reviews, and compliance activities.
-
To perform security reviews of infrastructure systems, cloud databases, virtualization platforms (including Windows, databases, backups, storage systems, and Active Directory).
-
To provide infrastructure security, core configuration, compliance documentation, remediation, and technical guidance.
-
To manage and administer DLP technologies and other security solutions.
GENERAL INFORMATION
-
Location: Karachi (unless otherwise specified)
-
Employment Type: Full-time
-
Equal Opportunity: NBP is an equal opportunity employer and welcomes applications from all qualified individuals, regardless of gender, religion, or disability.
-
Application Deadline: Applications must be submitted within 10 days from the date of publication of this advertisement.
-
How to Apply: Interested candidates may apply online through the NBP careers portal:
https://nbp.com.pk/careers
IMPORTANT NOTES
-
Only shortlisted candidates strictly meeting the above-mentioned basic eligibility criteria will be invited for panel interviews.
-
The bank reserves the right to accept or reject any application without assigning any reason.
-
No TA/DA will be admissible for the interview.
-
The employment will be on a contractual basis, and the compensation package will be market-based and commensurate with the candidate's qualification and experience.
National Bank of Pakistan
????? ???? ?? ???????
More Jobs for Unit Head
-
20-Sep-26 National Bank of Pakistan NBP
Wing Head
1 Jobs
-
Last Date
30-Sep-26
-
20-Sep-26 National Bank of Pakistan NBP
Relationship Manager
2 Jobs
-
Last Date
30-Sep-26
-
20-Sep-26 National Bank of Pakistan NBP
Group Chief Inclusive Development Group
1 Jobs
-
Last Date
30-Sep-26
-
20-Sep-26 National Bank of Pakistan NBP
Credit Officer
18 Jobs
-
Last Date
30-Sep-26
-
13-Sep-26 National Bank of Pakistan NBP
Personal Staff Officer
1 Jobs
-
Last Date
22-Sep-26